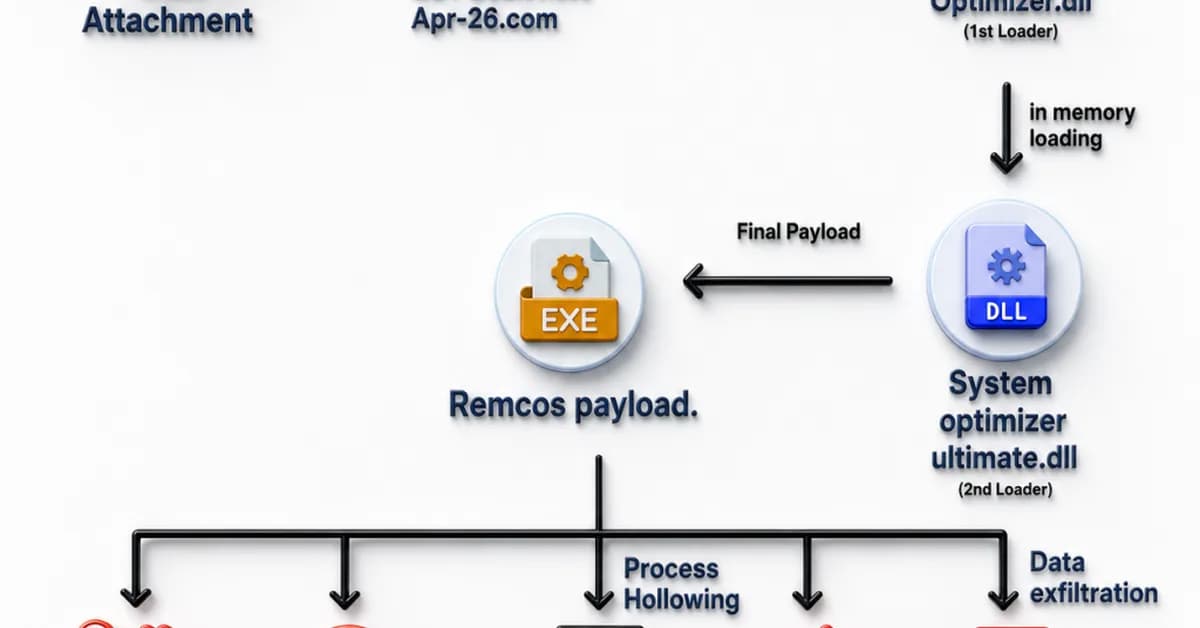
A sophisticated multi-stage steganographic loader campaign is distributing Remcos RAT and other malware payloads globally through phishing emails with India-specific filename decoys. The threat uses advanced evasion techniques including in-memory execution, embedded steganography, and process hollowing to bypass traditional security detection and forensic analysis. Infrastructure analysis suggests the loader operates as a malware-as-a-service platform, delivering diverse payload families including Agent Tesla, MassLogger, and Red Line Stealer.
Read the full article at Malware Analysis, News and Indicators - Latest topics
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views136

Ali NematiBlogUI.author_articles