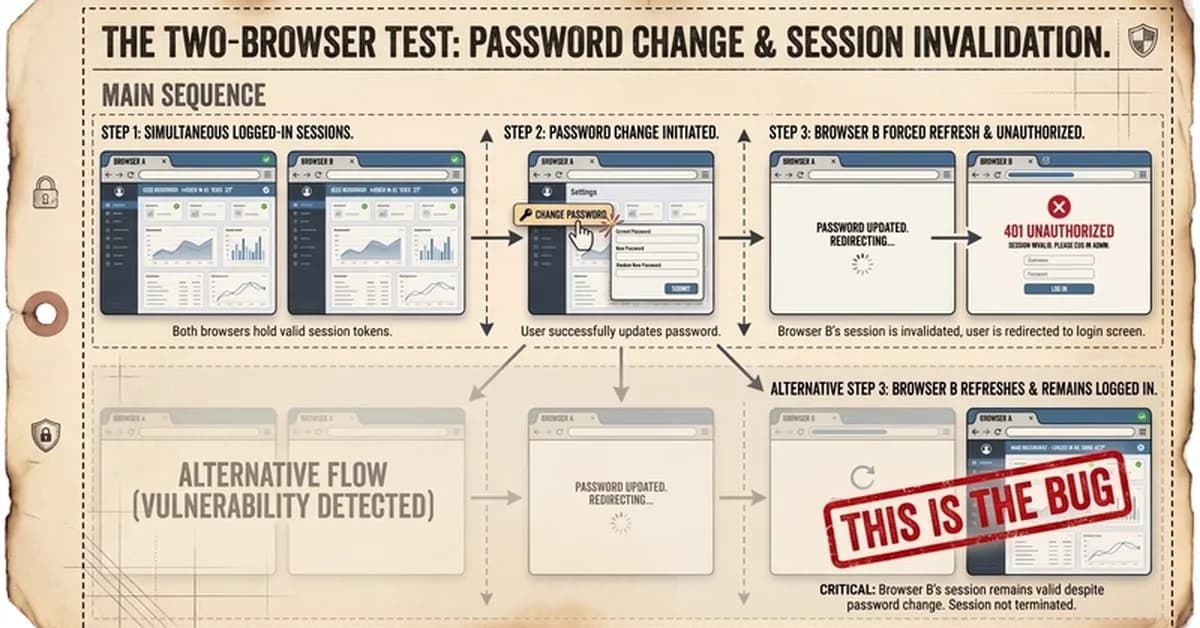
A common pitfall in security checklists is that they become performative exercises, where items are checked off without actual verification. A new approach reframes these checklists as executable tests, pairing each control with a specific, actionable verification step to ensure genuine security. This methodology, now integrated into a coding agent skill, aims to shift security considerations earlier in the development process and provide more reliable audit results, with a focus on concrete, verifiable actions rather than declarative statements.
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views2

Ali NematiBlogUI.author_articles