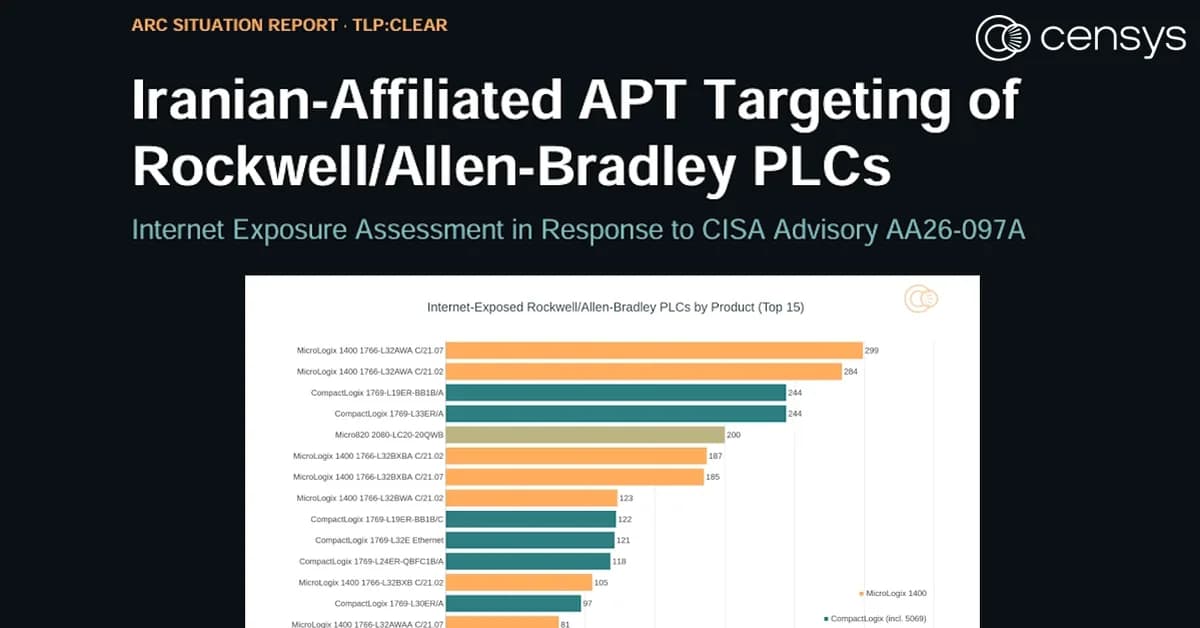
Censys research reveals Iranian-affiliated threat actors are actively exploiting internet-exposed Rockwell Automation Allen-Bradley PLCs, primarily in the U.S., to target critical infrastructure. This campaign leverages legitimate engineering tools and native protocols, complicating detection efforts while enabling manipulation of control systems without triggering traditional security measures.
Read the full article at Industrial Cyber
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views39

Ali NematiBlogUI.author_articles