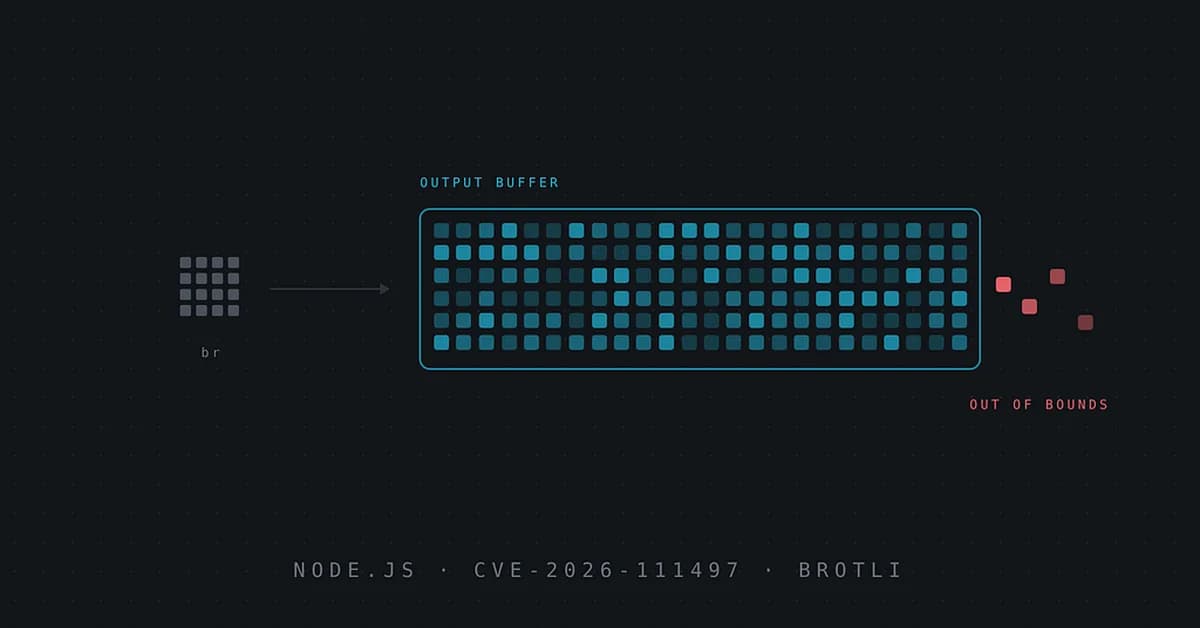
A critical vulnerability, CVE-2026-111497, has been identified in the Node.js Brotli decoder, enabling remote code execution. This poses a significant risk to cybersecurity professionals because Node.js is widely used for backend infrastructure, APIs, and AI tooling, and the vulnerability is triggered by data downloaded by the server itself, not just user-supplied input. Organizations should immediately upgrade to versions 22.23.4, 24.22.1, or 26.12.1 and review any features that fetch external URLs.
Read the full article at System Weakness - Medium
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views0

Ali NematiBlogUI.author_articles