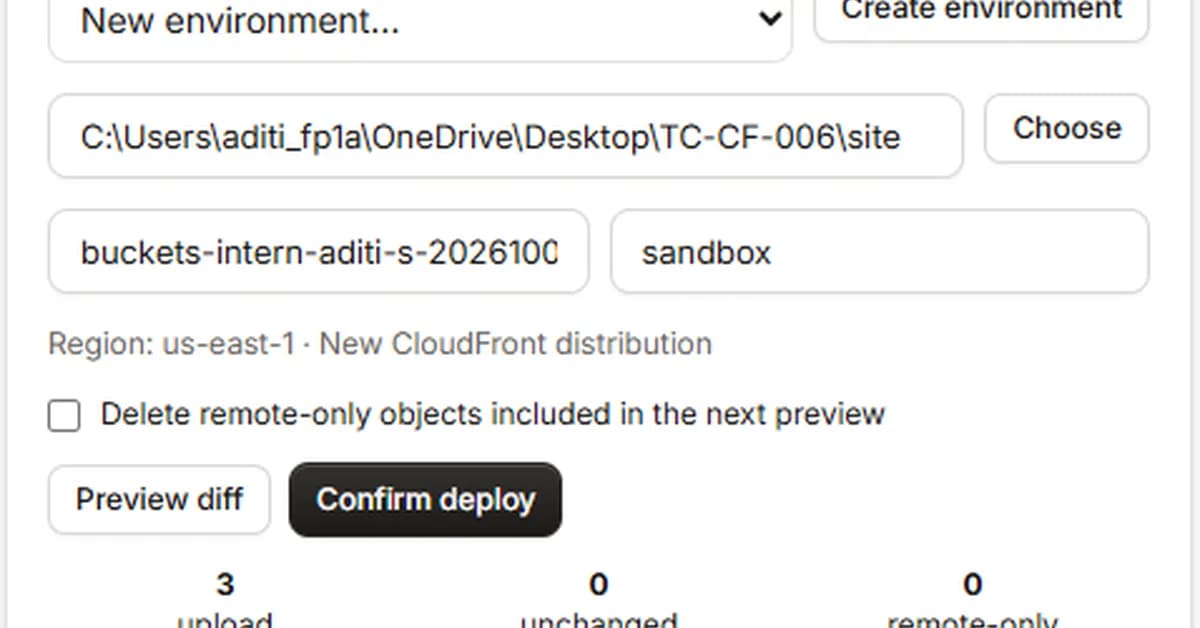
A tutorial demonstrates how to deploy a static website with a private S3 origin accessible via CloudFront, ensuring content is publicly available through HTTPS while restricting direct access to the S3 bucket. This approach enhances security by preventing anonymous object reads. It's relevant for developers seeking to secure static site origins without sacrificing public accessibility. Future implications may involve further integration of such private origin setups with content delivery networks for robust web hosting.
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views46
Tags

Ali NematiBlogUI.author_articles