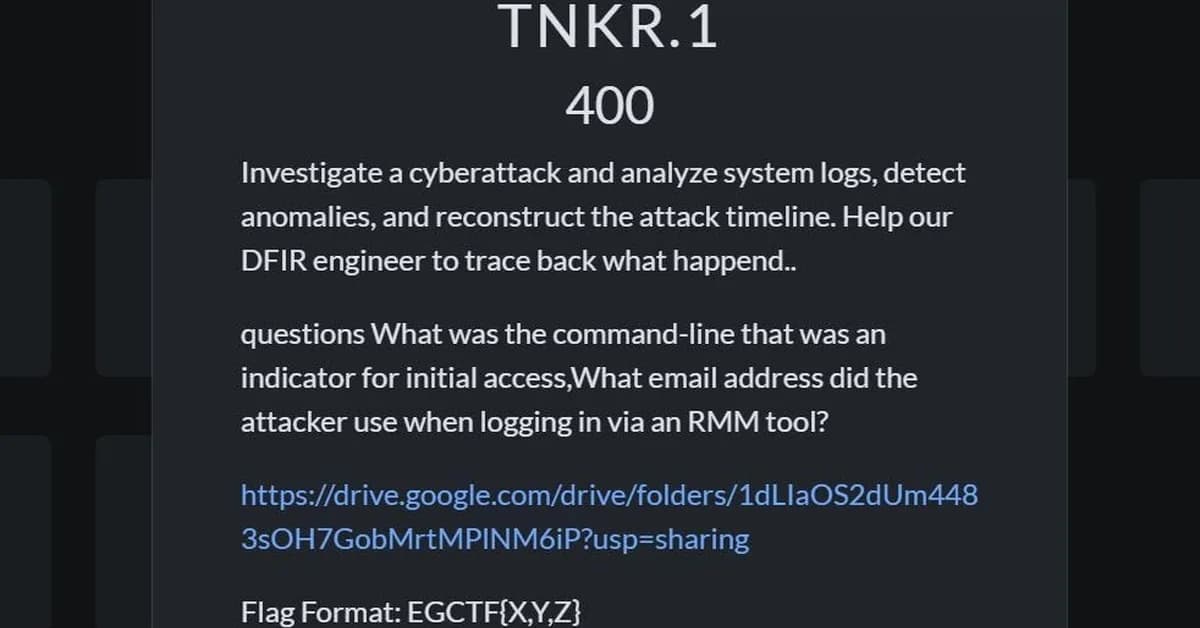
In the EGCTF 2025 Qualifications "TNKR.1" challenge, participants analyzed Windows PowerShell logs from compromised devices to identify malicious commands and an email address linked to a trojan infection. This exercise highlights the importance of forensic analysis in detecting initial access vectors used by attackers.
Security professionals should focus on log timeline analysis and automated script usage for efficient threat hunting.
Read the full article at InfoSec Write-ups - Medium
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views106

Ali NematiBlogUI.author_articles