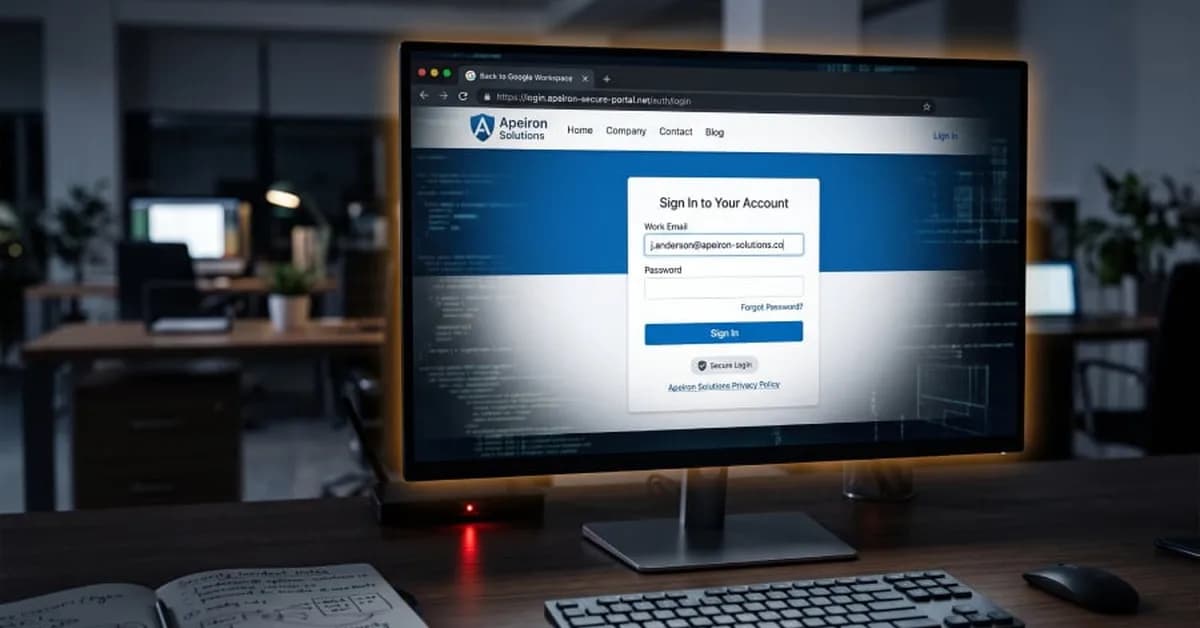
Attackers are using legitimate Google services as a proxy in phishing campaigns to steal Microsoft credentials, making it harder for security systems to detect the malicious activity. This tactic personalizes phishing pages and bypasses initial security checks by leveraging trusted domains, posing significant risks to corporate targets across various industries. Security teams must vigilantly monitor for suspicious authentication activities and unauthorized remote access tools like ScreenConnect to mitigate potential damage.
Read the full article at eSecurityPlanet
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views39

Ali NematiBlogUI.author_articles