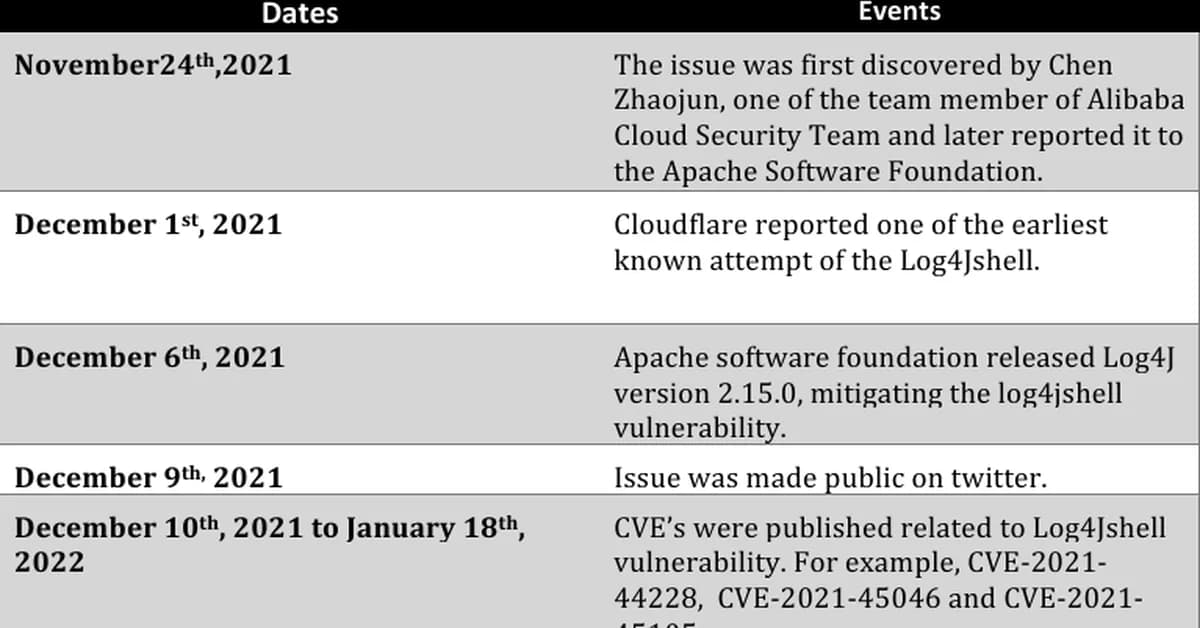
A critical vulnerability, CVE-2021-44228 (dubbed Log4Shell), was discovered in Apache Log4j 2, a widely used Java logging library. This flaw allows attackers to execute code remotely on affected servers, potentially granting them unauthorized access – impacting organizations like Cloudflare, Apple, and Minecraft. The vulnerability stems from an insecure feature called JNDI lookups, which enables the injection of malicious LDAP requests into log messages, highlighting the importance of secure coding practices and careful configuration within Java-based systems.
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views13

Ali NematiBlogUI.author_articles