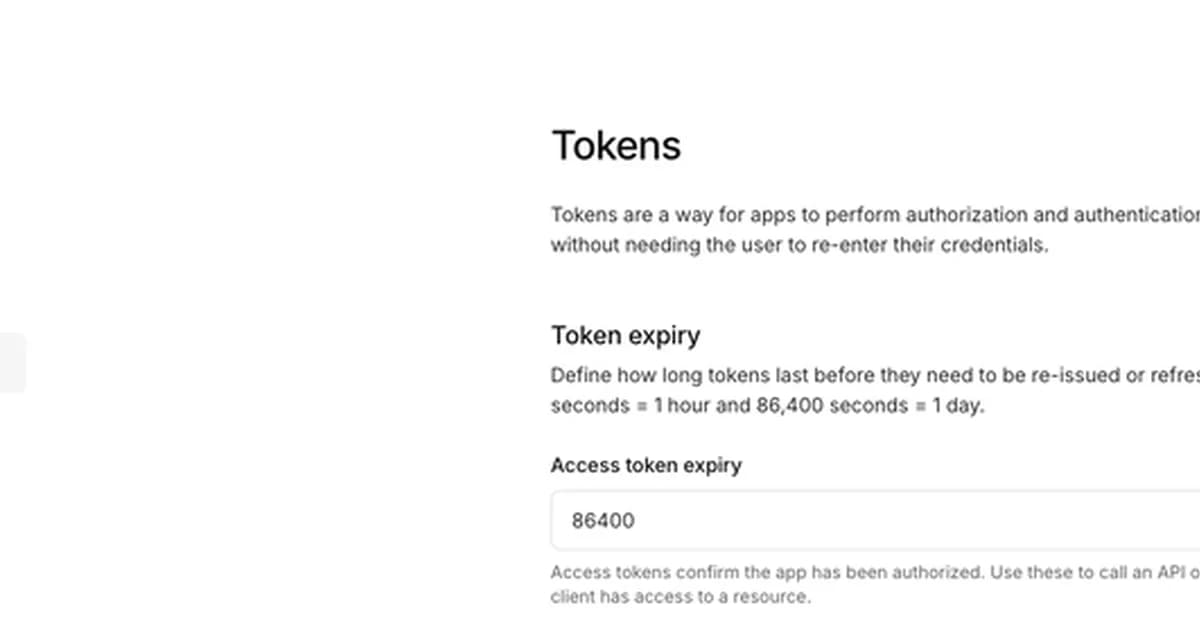
AI agents can maintain access even if their keys are compromised by using tokens with long expiration times. To mitigate this, agents should be designed to periodically re-authenticate and obtain new, short-lived access tokens. This practice ensures that any leaked token quickly becomes invalid, preventing prolonged unauthorized access.
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views2
Tags

Ali NematiBlogUI.author_articles