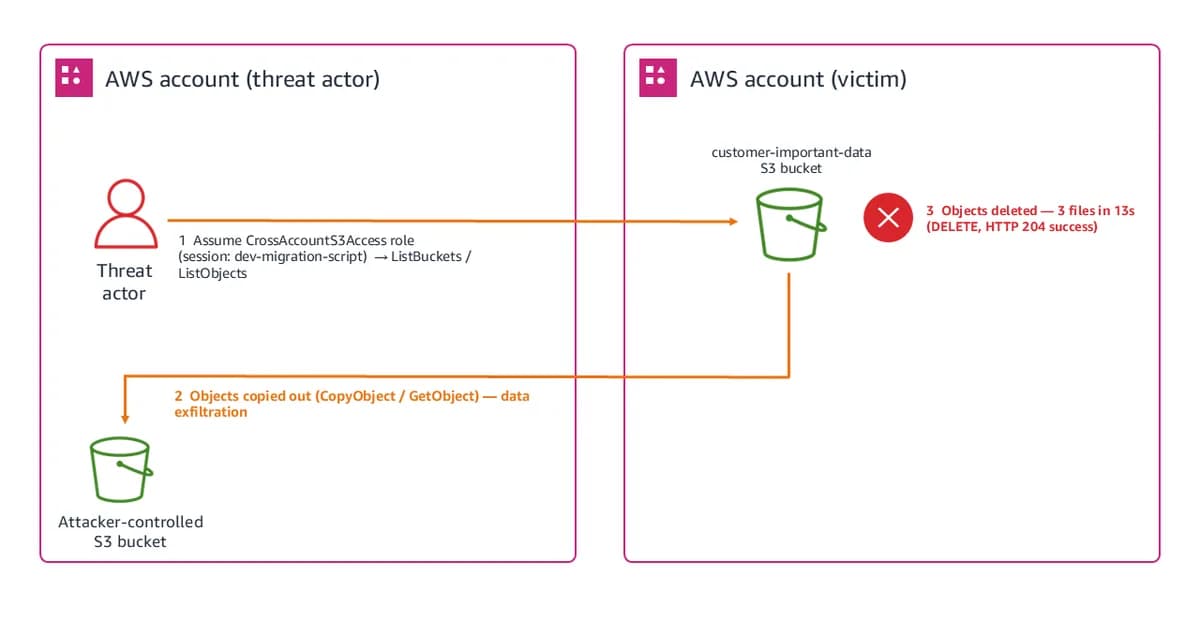
Given the detailed timeline and analysis provided, here are the key investigation priorities and response actions to address the incident involving unauthorized deletion of critical data from an Amazon S3 bucket:
Investigation Priorities
-
Access Gaining Mechanism:
- Examine the trust policy of the
CrossAccountS3Accessrole. - Review authentication events in both the trusting account and trusted accounts.
- Investigate other sessions using the same role around the same timeframe to identify potential lateral movement.
- Examine the trust policy of the
-
Data Exposure Assessment:
- Search for
GetObjectoperations on the deleted objects before their deletion time. - Look into unusual network traffic patterns during the reconnaissance phase.
- Identify any
CopyObjectactivities that might indicate data theft prior to destruction.
- Search for
-
Business Impact Analysis:
- Determine why these specific files were targeted (financial report, PII database, production backup).
- Assess regulatory notification requirements for the exposure of personally identifiable information (PII).
- Evaluate business disruption from the loss of critical backups and financial reports.
Response Checklist
- Assess Legitimacy of Cross-Account Access:
- Verify if there is a legitimate business purpose served by this cross
Read the full article at AWS Security Blog
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views55
On this page

Ali NematiBlogUI.author_articles