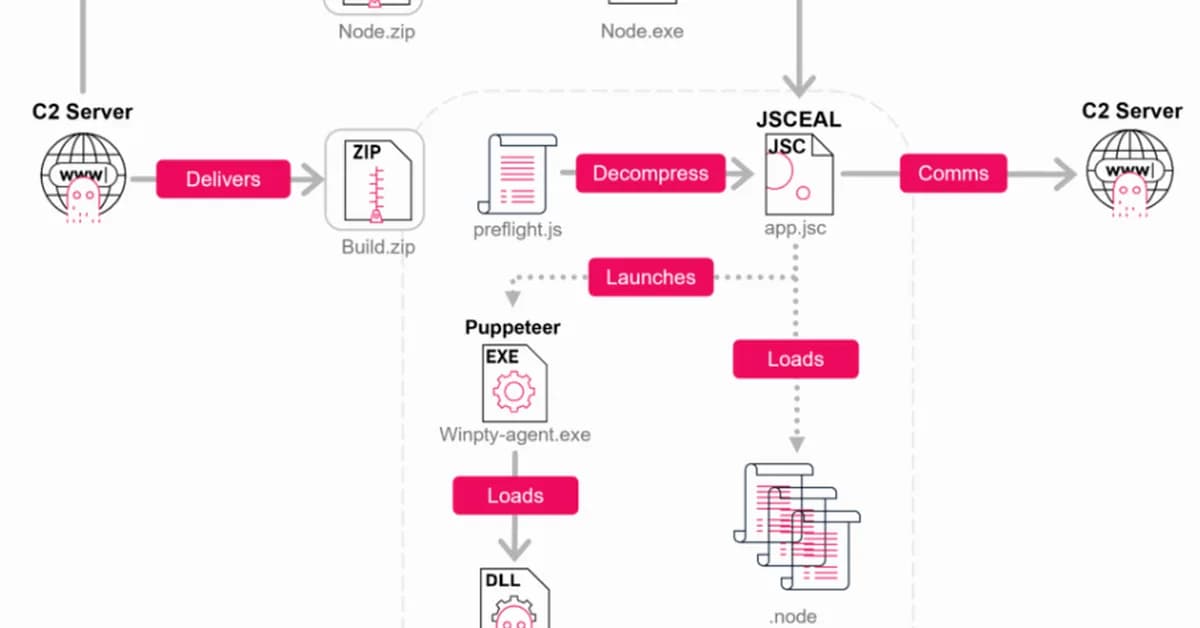
Researchers have developed a tool to decompile V8 bytecode used by the JSCeal malware, which steals cryptocurrency by hiding its malicious code. This advancement allows for the analysis of previously obfuscated malware, revealing sophisticated theft techniques like credential harvesting and HTTPS traffic interception. For developers and security professionals, this highlights the importance of robust deobfuscation tools and understanding advanced malware evasion tactics.
Read the full article at Security Affairs
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views18
Ali NematiBlogUI.author_articles