This article discusses the importance of security in software development, highlighting a tool called Kiro that helps developers write more secure code by default. The author presents three common vulnerabilities: SQL injection, cross-site scripting (XSS), and command injection, and demonstrates how Kiro addresses these issues.
Key Points:
-
Security as Default:
- Security should be the default mindset in software development.
- Developers often overlook security due to time constraints or lack of experience with secure coding practices.
-
Kiro Tool Introduction:
- Kiro is an IDE extension that helps developers write secure code by providing automatic fixes for common vulnerabilities.
- It integrates seamlessly into existing workflows, enhancing developer productivity and reducing the risk of introducing security flaws.
-
Vulnerability Examples:
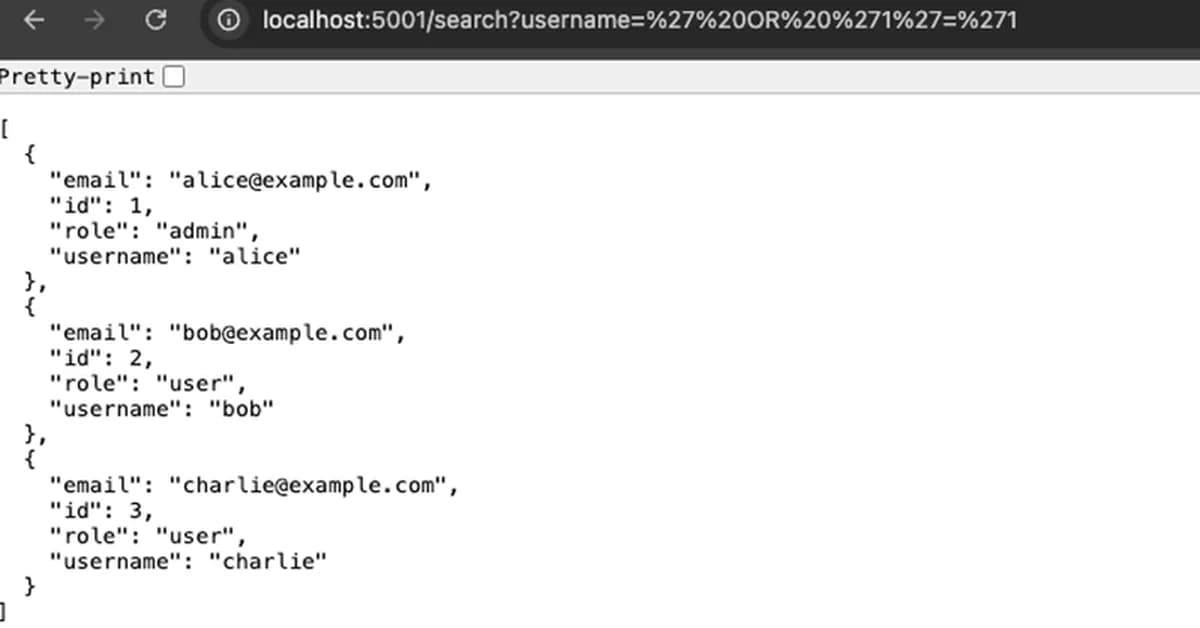
- SQL Injection:
- Vulnerable Code: A Python Flask application with a query that directly uses user input without sanitization.
- Kiro Fix: Uses parameterized queries to prevent SQL injection by ensuring that user inputs are treated as data rather than executable code.
python1# Vulnerable Code: 2@app.route('/search') 3def search(): 4 query = request.args.get('query', '') - SQL Injection:
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views261
Tags
On this page

Ali NematiBlogUI.author_articles