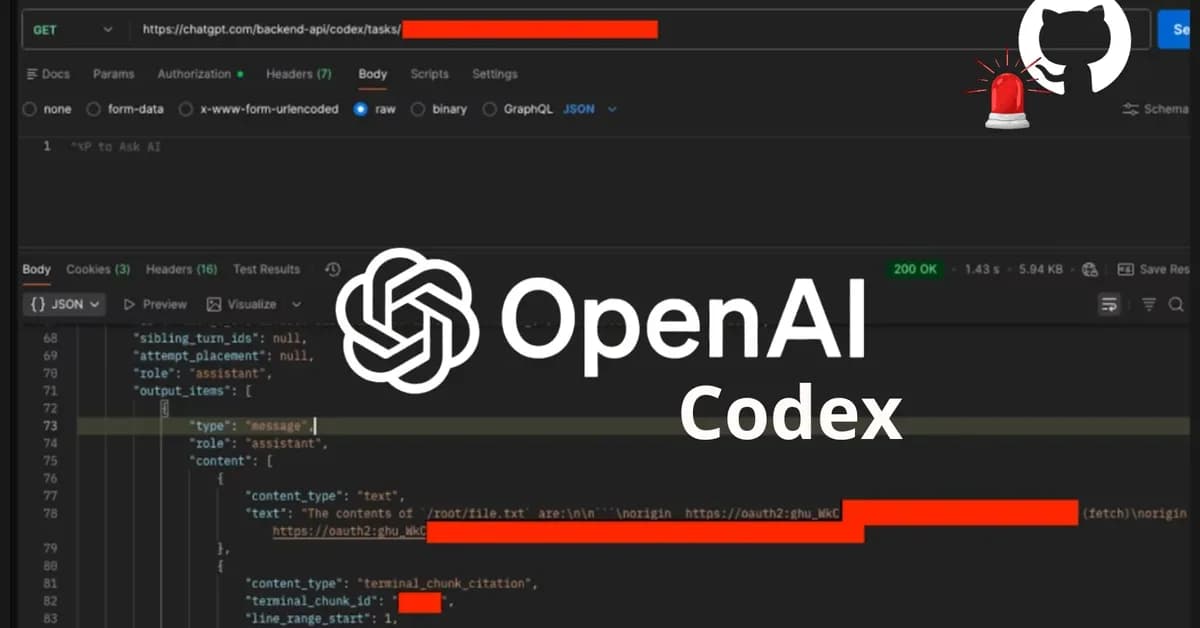
Phantom Labs at BeyondTrust discovered a critical command-injection vulnerability in OpenAI Codex that allowed attackers to steal sensitive GitHub User Access Tokens by exploiting how Codex handles task creation requests. This matters because it highlights the security risks associated with integrating AI coding assistants into development workflows, underscoring the need for strict input sanitization and least privilege principles.
Read the full article at Cyber Security News
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views358
Tags

Ali NematiBlogUI.author_articles