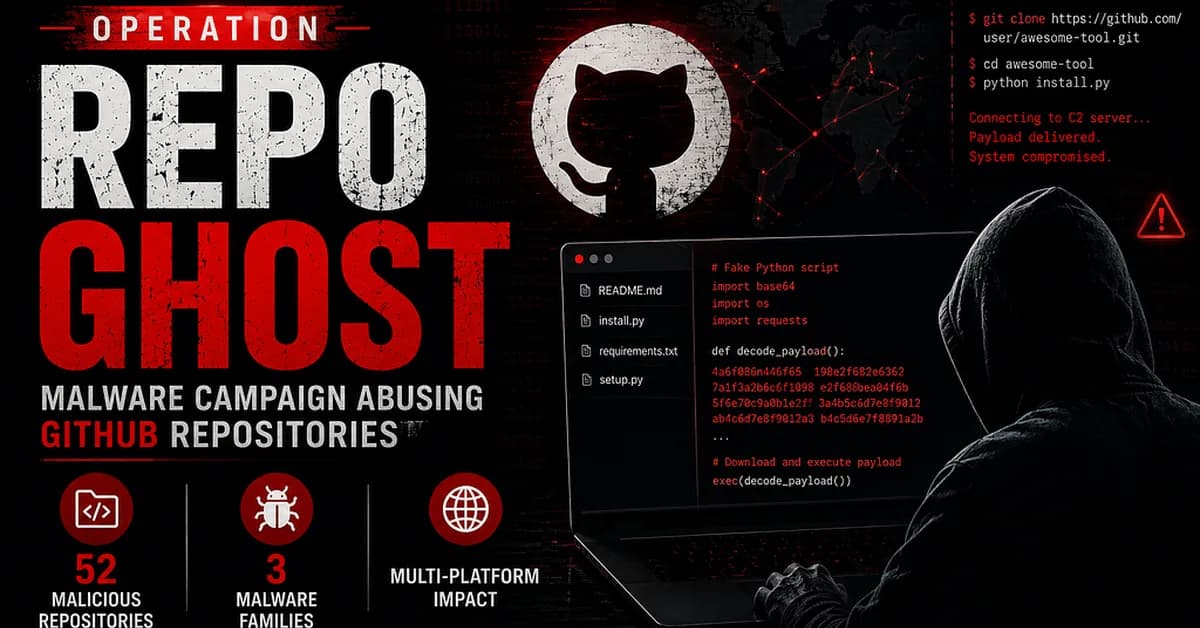
Operation RepoGhost reveals a Russian-linked malware campaign distributing custom Go-based infostealers through fake GitHub repositories impersonating legitimate projects. The campaign has evolved from targeting Windows to consolidating on a single, sophisticated infostealer that steals various sensitive data. This underscores the persistent threat of supply chain attacks and the need for developers and security teams to rigorously vet open-source code and repository origins.
Read the full article at InfoSec Write-ups - Medium
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views71

Ali NematiBlogUI.author_articles