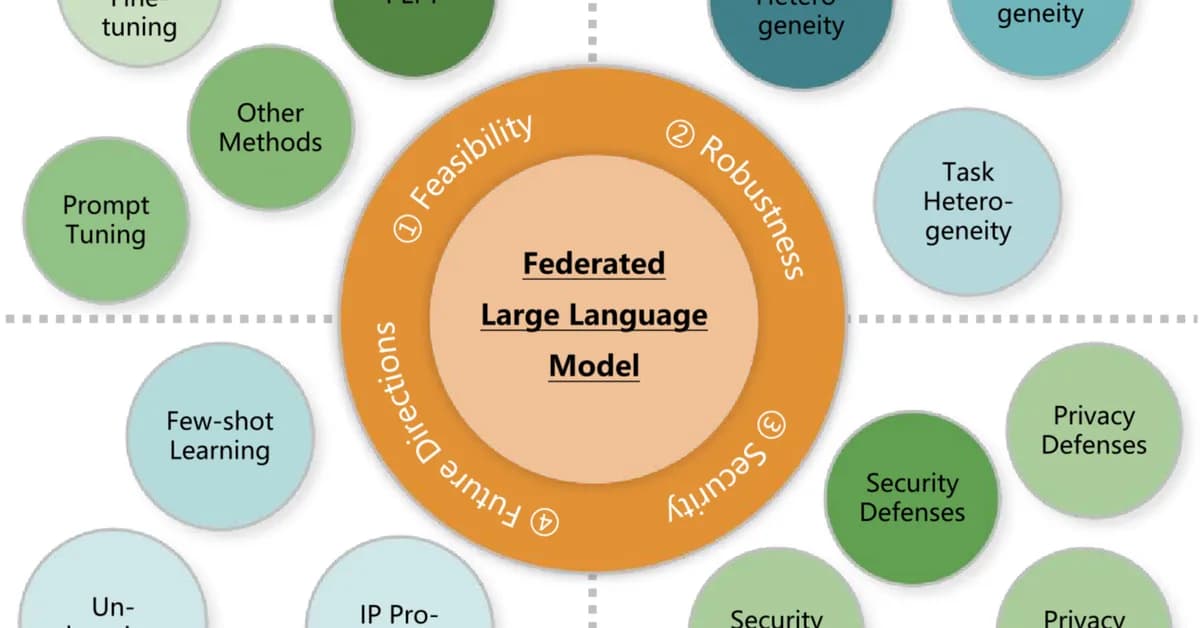
Researchers from Nemati AI have introduced Safe-FedLLM, a framework designed to enhance security in federated learning for large language models by identifying and mitigating attacks from malicious clients through lightweight classifiers. This development is crucial for developers and tech professionals as it addresses the growing concern of security vulnerabilities in open federated environments, ensuring more robust and reliable training processes without compromising performance or efficiency.
Read the full article at arXiv cs.CR (Cryptography & Security)
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views131

alinemati1983-6987BlogUI.author_articles