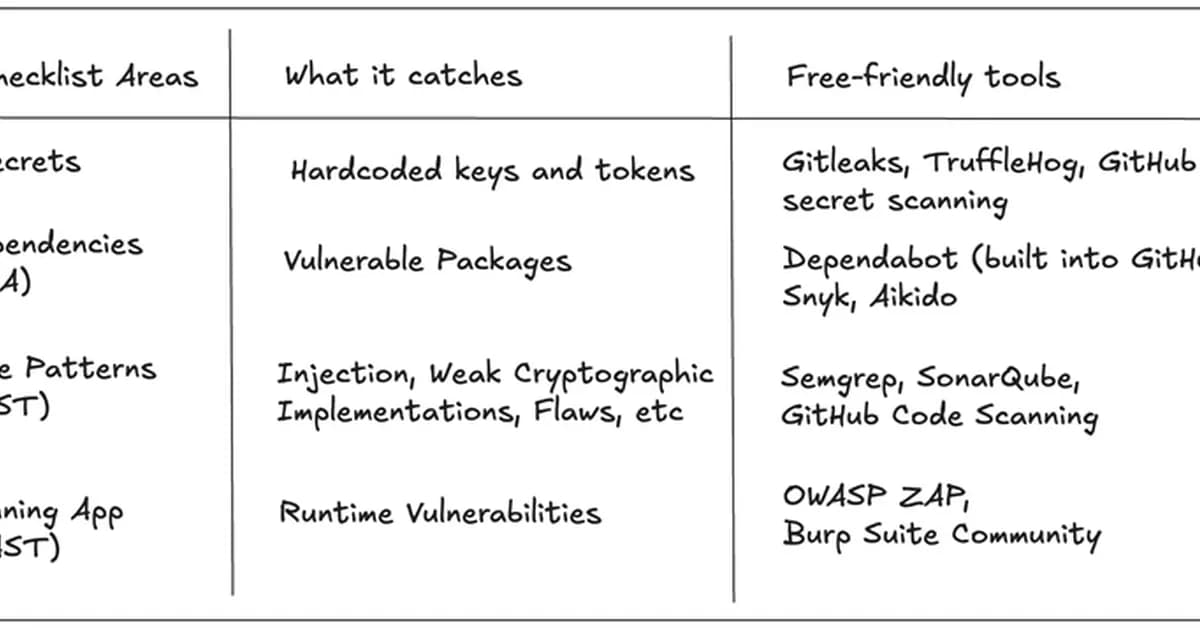
The rise of AI coding assistants allows for rapid application development, offering a significant competitive advantage for teams. However, this speed introduces security concerns as AI-generated code often bypasses traditional peer review processes, potentially shipping vulnerabilities directly to production. To mitigate these risks, a thorough security checklist is crucial, focusing on areas like secret management, dependency verification, and input validation, as AI models can perpetuate insecure patterns and even hallucinate non-existent packages.
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views25

Ali NematiBlogUI.author_articles