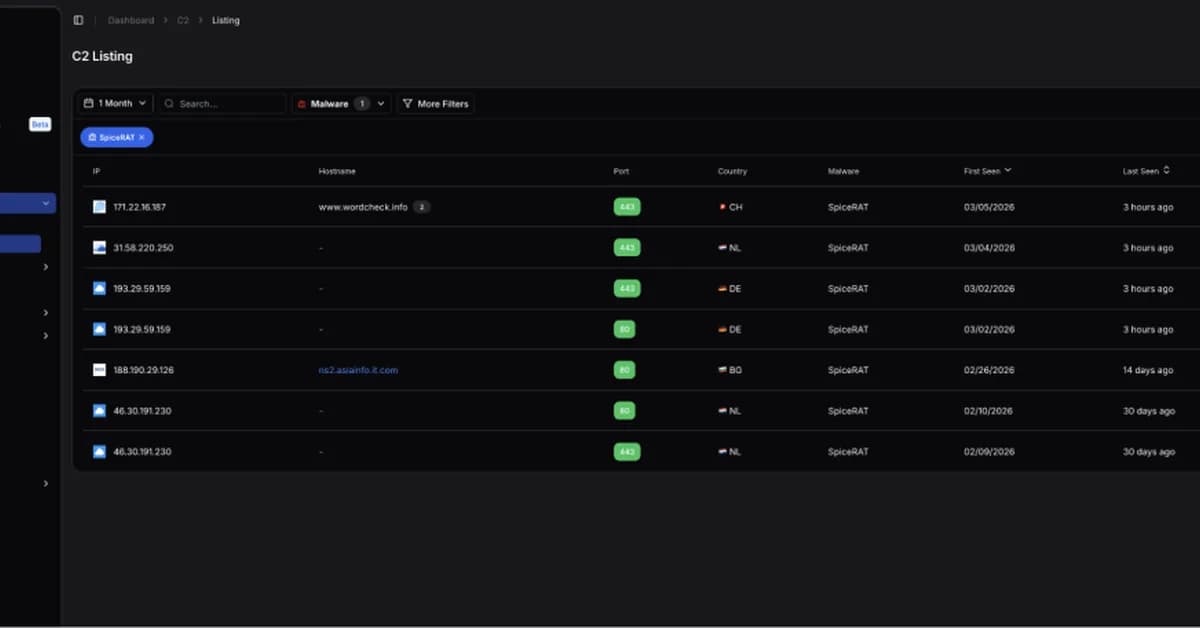
Researchers have linked SpiceRAT, NodeEdgeRAT, and NomadRAT malware families to a four-year campaign called SilkParasite targeting governments and critical sectors in Central Asia. This discovery highlights the importance of infrastructure analysis – examining shared certificates, domains, and hosting patterns – as an alternative to traditional malware sample analysis for detecting sophisticated campaigns. Organizations operating in affected regions should prioritize monitoring their networks for associated indicators, including those related to a certificate impersonating Uzbekistan’s railway authority issued by a Chinese-linked entity.
Read the full article at Security Affairs
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.