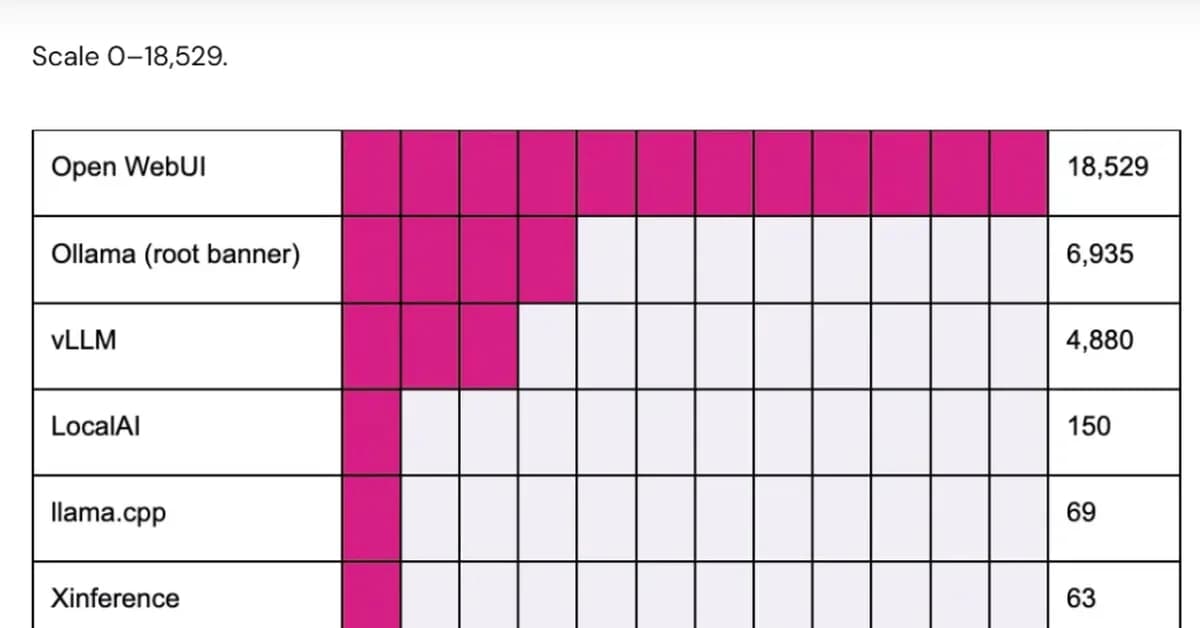
Researchers have identified over 36,000 publicly accessible AI endpoints, a significant number lacking even basic HTTP authentication. This exposes organizations to resource abuse – allowing others to utilize their hardware and models without permission – and creates opportunities for credential theft if these systems connect to other internal resources. Cybersecurity teams should immediately scan their environments to identify any exposed AI infrastructure and implement network-layer security controls as a critical first step in mitigating this risk.
Read the full article at Security Affairs
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views21

Ali NematiBlogUI.author_articles