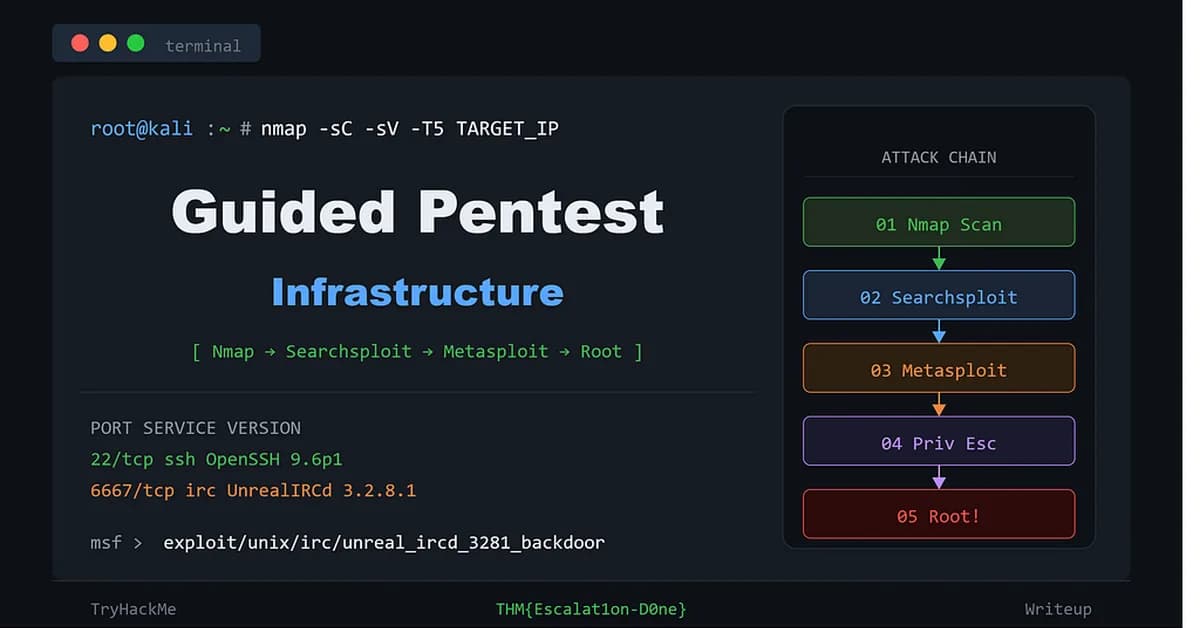
The walkthrough provided outlines a comprehensive penetration testing process for a machine named "Pentest Target" on TryHackMe. Here's a summary of the key steps and findings:
Enumeration
- Nmap Scan: Conducted an initial Nmap scan using
nmap -sC -sV <TARGET_IP>to identify open ports, services, and versions.- Open Ports: 22 (SSH), 80 (HTTP), 6667 (IRC)
- Services: Apache HTTP Server, SSH, Unreal IRCd
Vulnerability Research
- Searchsploit: Used searchsploit to find known vulnerabilities for the services identified in the Nmap scan.
- Found a critical vulnerability in Unreal IRCd version 3.2.8.1.
Initial Access
- Exploitation with Metasploit:
- Chose
unix/irc/unreal_ircd_3281_backdoorexploit from Metasploit. - Set the payload to
cmd/unix/reverse. - Configured options: RHOSTS, LHOST, and LPORT.
- Exploited the IRC server using the backdoor
- Chose
Read the full article at InfoSec Write-ups - Medium
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views100
On this page

Ali NematiBlogUI.author_articles