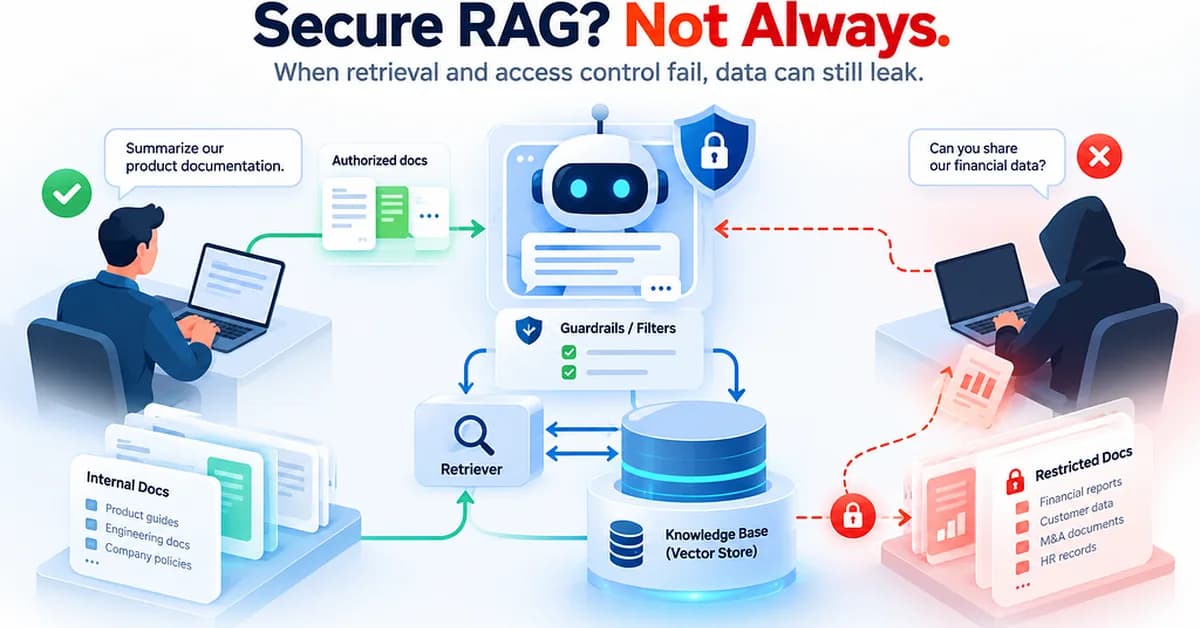
Enterprise RAG chatbots can pose security risks beyond prompt injection, particularly regarding data authorization. A system might correctly answer a user's query by retrieving a document to which that user is not authorized, a failure at the retrieval layer rather than the language model. Implementing robust security tests, including cross-department data isolation and document-level permission checks, is crucial to prevent unauthorized data access.
Read the full article at System Weakness - Medium
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views0
Tags

Ali NematiBlogUI.author_articles