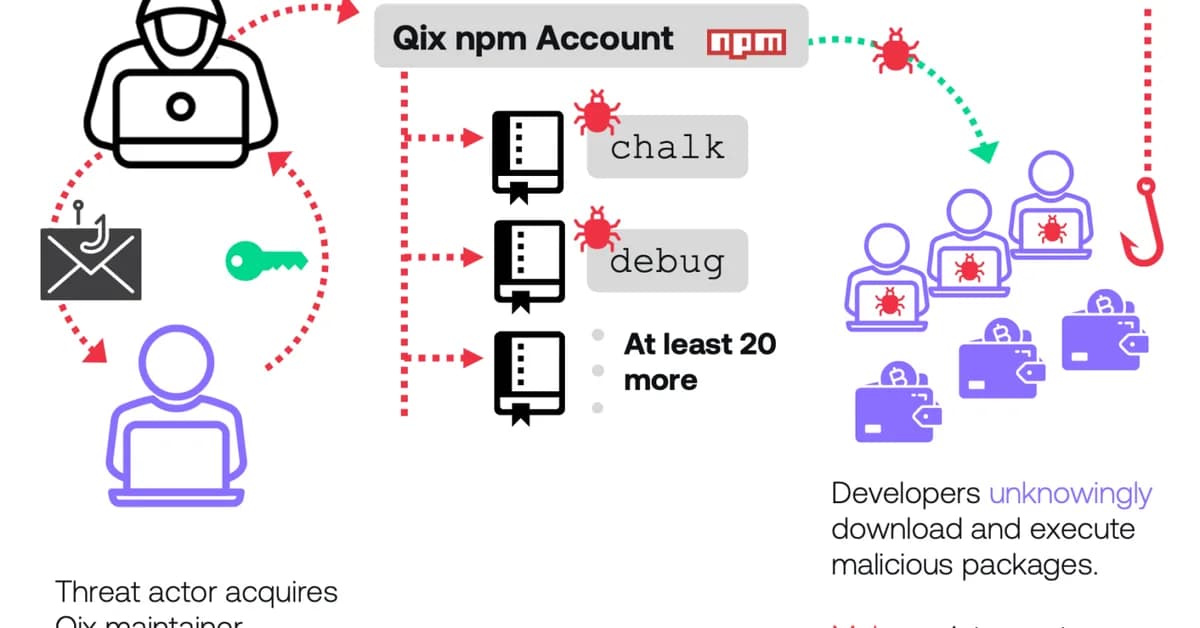
Attackers compromised the Trivy GitHub Action in March 2026, stealing cloud credentials from workflows that used it. This attack is part of a series of CI/CD supply chain breaches targeting cloud secrets since November 2024. Developers must implement security measures like SHA pinning and egress monitoring to protect their workflows and prevent similar attacks.
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views406

Ali NematiBlogUI.author_articles