Axios NPM Supply Chain Attack: Comprehensive Incident Response and Prevention Guide
Table of Contents
- Overview
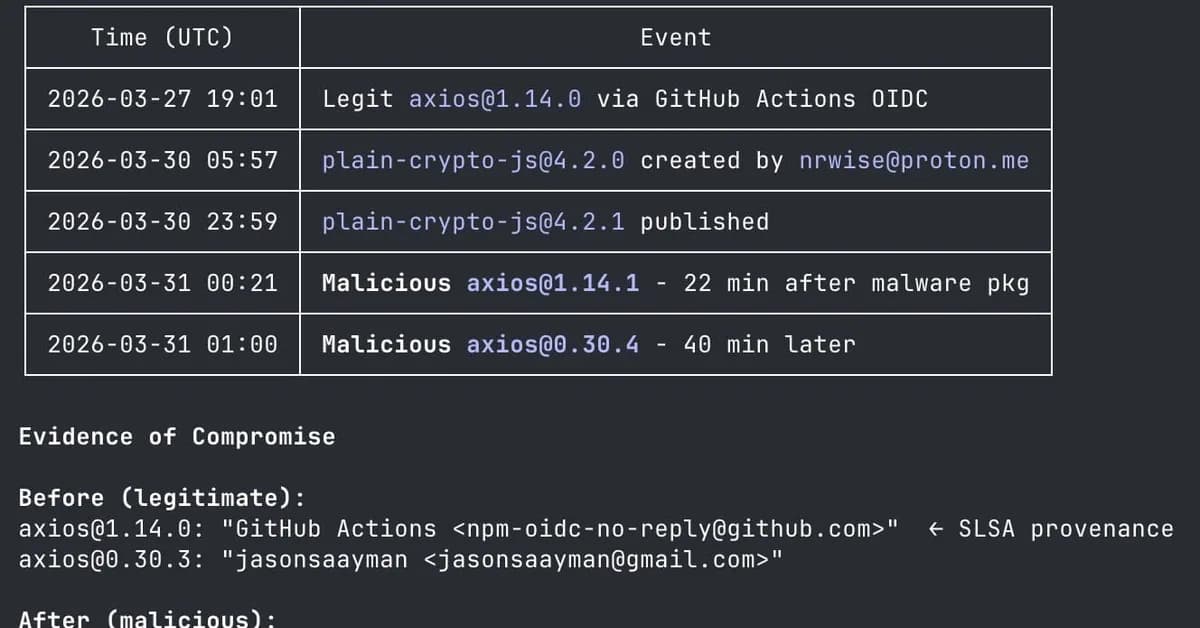
- Incident Timeline
- Attack Details
- Detection Methods
- Remediation Steps
- Business Impact
- Preventive Measures
1. Overview
The Axios NPM Supply Chain Attack is a significant security incident where malicious versions of the popular Axios library were published, potentially compromising millions of installations and leading to credential theft, lateral movement, and intellectual property theft.
2. Incident Timeline
- March 30, 2026: Malicious versions of Axios (1.14.1) and a hidden dependency (
[email protected]) were published. - April 1, 2026: The security community began to detect the malicious packages.
- April 3, 2026: A community incident scanner was released to help organizations identify affected systems.
3. Attack Details
The attackers exploited a hidden dependency in Axios to inject malware that could steal credentials and exfiltrate sensitive data. The attack leveraged npm's default
Read the full article at SOCRadar-? Cyber Intelligence Inc.
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views161
On this page
Ali NematiBlogUI.author_articles