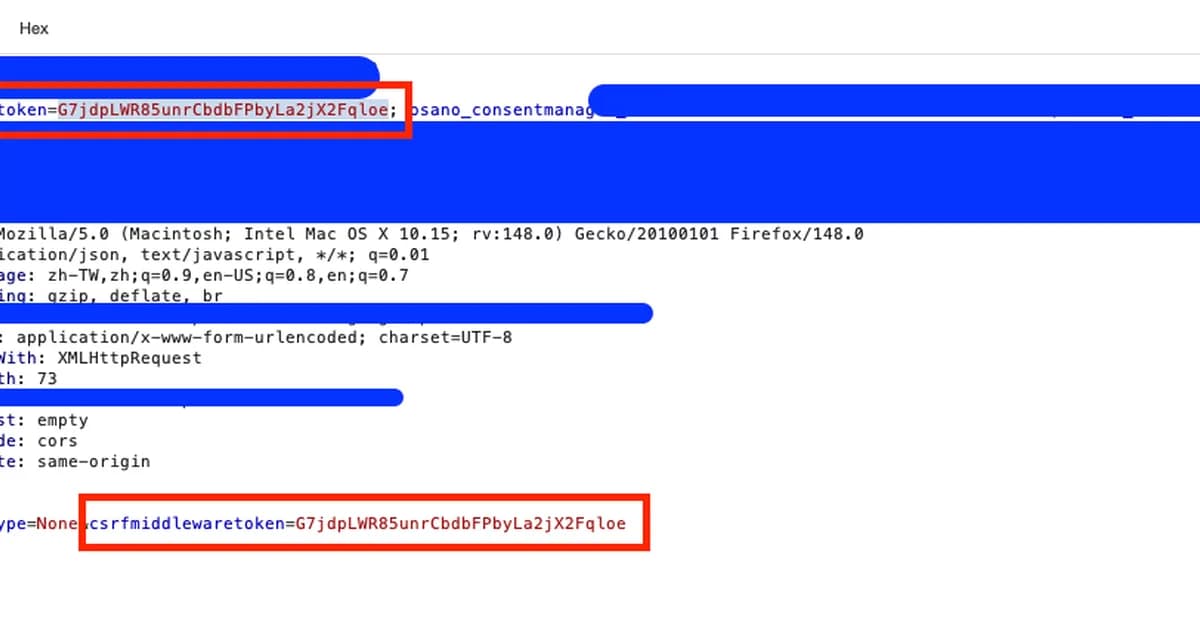
During an internal penetration test of a Django-based application, it was discovered that CSRF tokens can be bypassed with any value, raising security concerns. However, this behavior is actually expected due to Django’s design, which relies on token consistency rather than validation of the token's origin. This highlights the importance of proper cookie and browser protections to mitigate risks associated with misconfigurations or misunderstandings of Django’s CSRF implementation.
Read the full article at InfoSec Write-ups - Medium
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views39

Ali NematiBlogUI.author_articles