The article discusses a series of vulnerabilities found in an application that allowed an unauthenticated attacker to escalate privileges and access sensitive data across multiple organizations. Here's a summary of the key points:
-
Hidden Signup: The signup button was hidden on the frontend, but the backend still accepted signups.
-
Public JavaScript Configuration: The application exposed configuration variables like
USER_SIGNUP: falsein public JavaScript files. -
Signup API: Despite the hidden signup button, the
/people/endpoint allowed new users to register. -
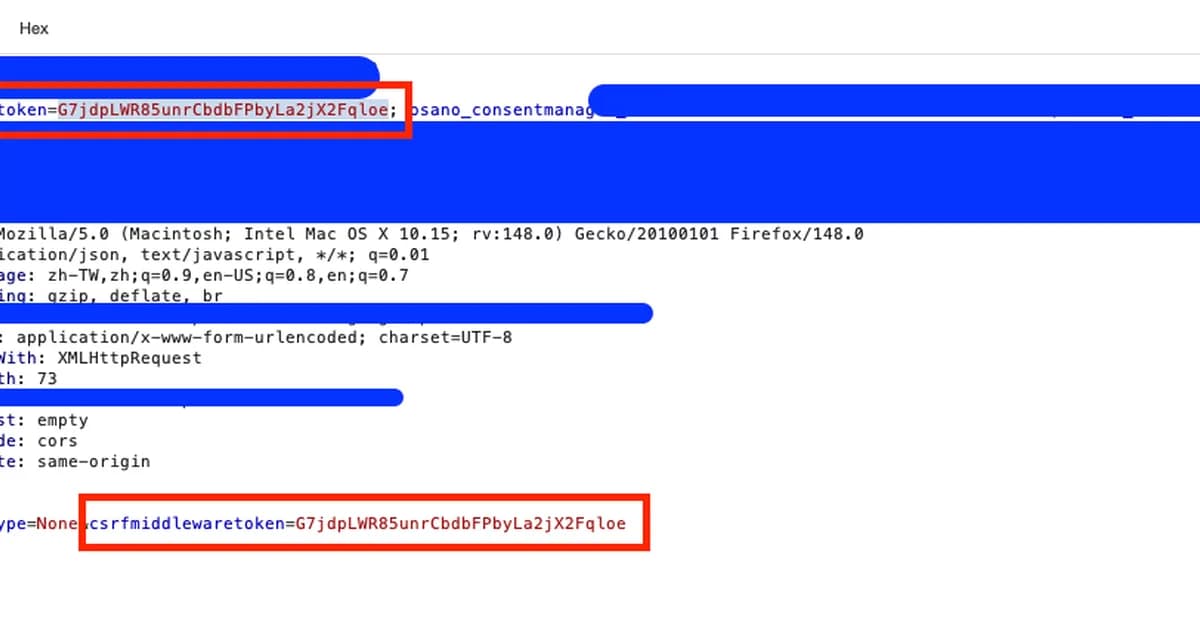
Confirmation Token: Upon signing up, a confirmation token was returned in the response instead of being sent via email for verification.
-
Authentication Token: The attacker could use the confirmation token to authenticate and obtain an authentication token.
-
Privilege Escalation: By modifying their user profile through the
/people/{uuid}/endpoint, users could setis_staff: true, granting administrative privileges. -
Tenant Isolation Testing: With staff-level access, the attacker tested if the API correctly enforced tenant boundaries and found that it did not, allowing cross-tenant enumeration of users.
-
Domain API Keys Exposure: The
/domains/endpoint exposed sensitive information such
Read the full article at InfoSec Write-ups - Medium
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.