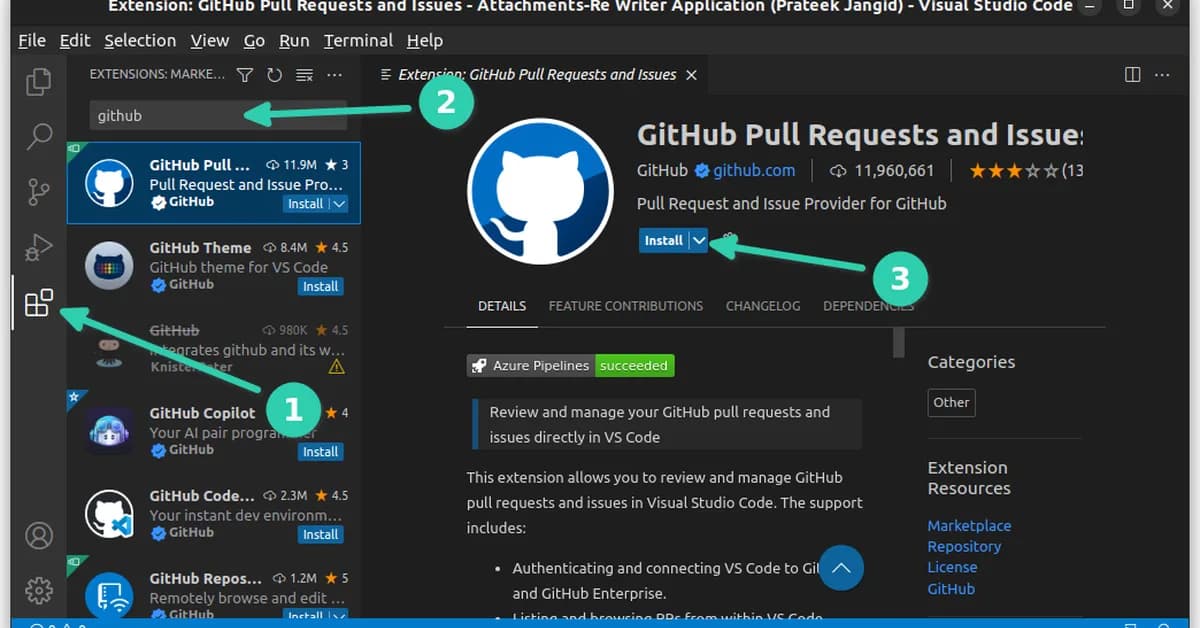
A recent GitHub attack, codenamed Megalodon, saw over 5,000 malicious commits pushed to repositories within six hours, highlighting the need for enhanced security measures in software development environments. This underscores the vulnerability of code repositories and CI/CD pipelines to sophisticated attacks that can compromise credentials and source code, posing significant risks to enterprises relying on these platforms.
Read the full article at Malware Analysis, News and Indicators - Latest topics
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views390

Ali NematiBlogUI.author_articles