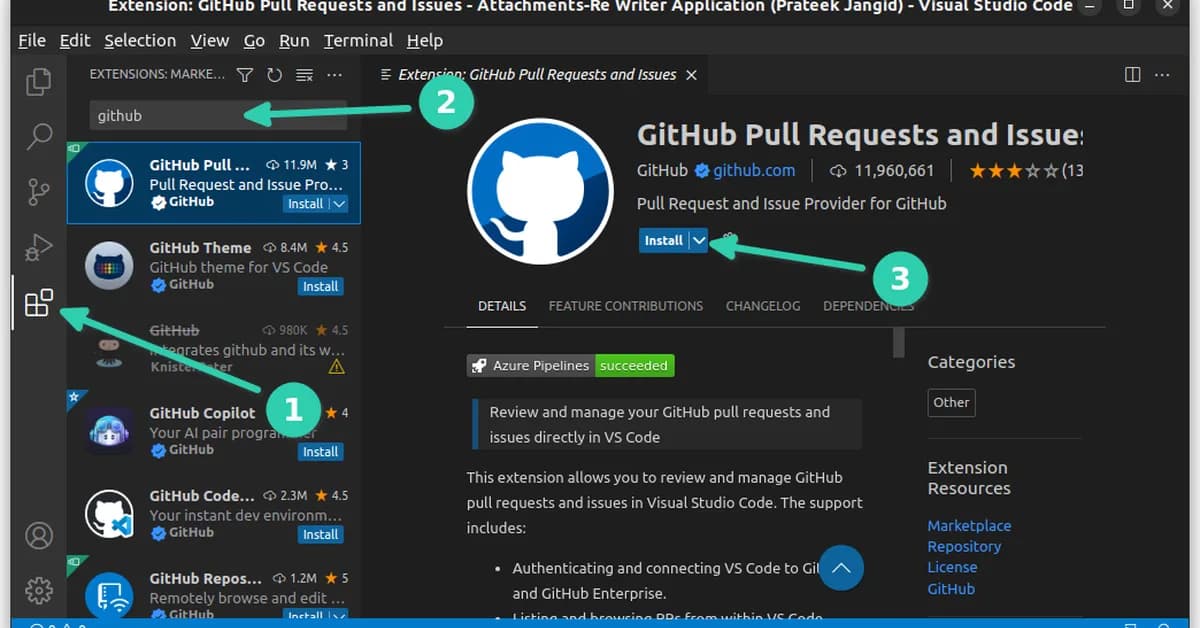
GitHub confirmed that internal repositories were compromised after an employee's device was infected by a malicious Visual Studio Code extension, highlighting the increasing risks to software development platforms and third-party tools. This incident underscores the vulnerability of developer environments, as a single compromised account or tool can provide access to numerous downstream systems, emphasizing the need for enhanced security measures in development ecosystems.
Read the full article at CyberScoop
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views374

Ali NematiBlogUI.author_articles