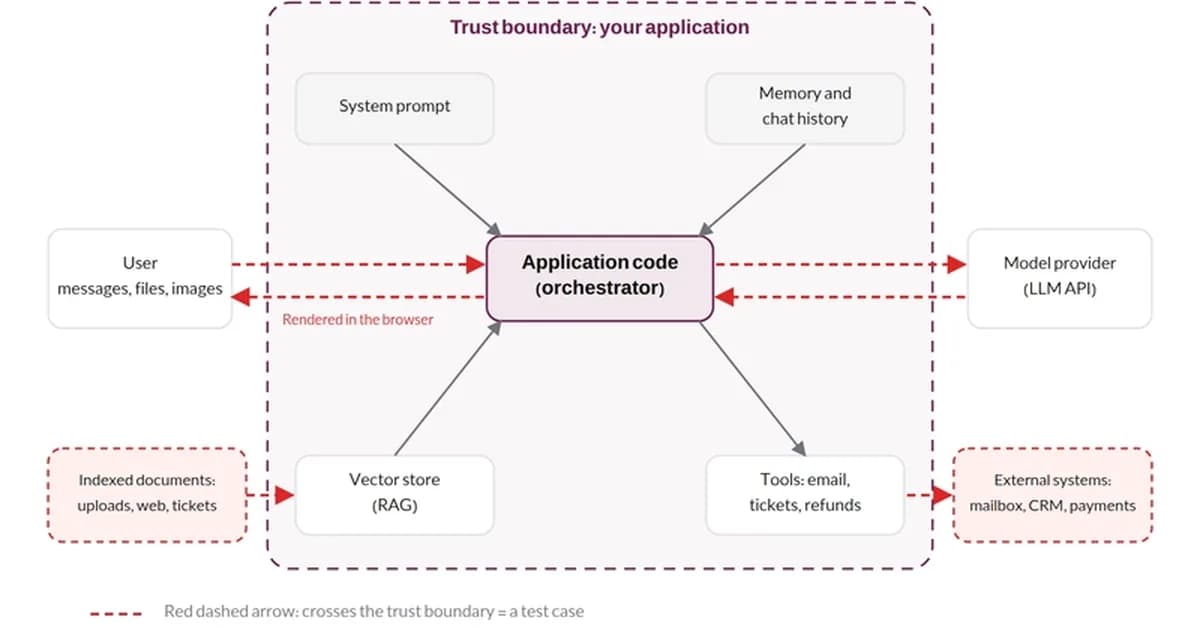
Security testing for LLM applications must extend beyond traditional web assessments to address the unique vulnerabilities introduced by the models themselves. The core challenge lies in the inability of LLMs to reliably distinguish instructions from data, opening avenues for prompt injection and data leakage. A comprehensive testing strategy involves mapping the data flow and scrutinizing every boundary where untrusted text enters the model's context or the model's output becomes untrusted input.
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views40

Ali NematiBlogUI.author_articles