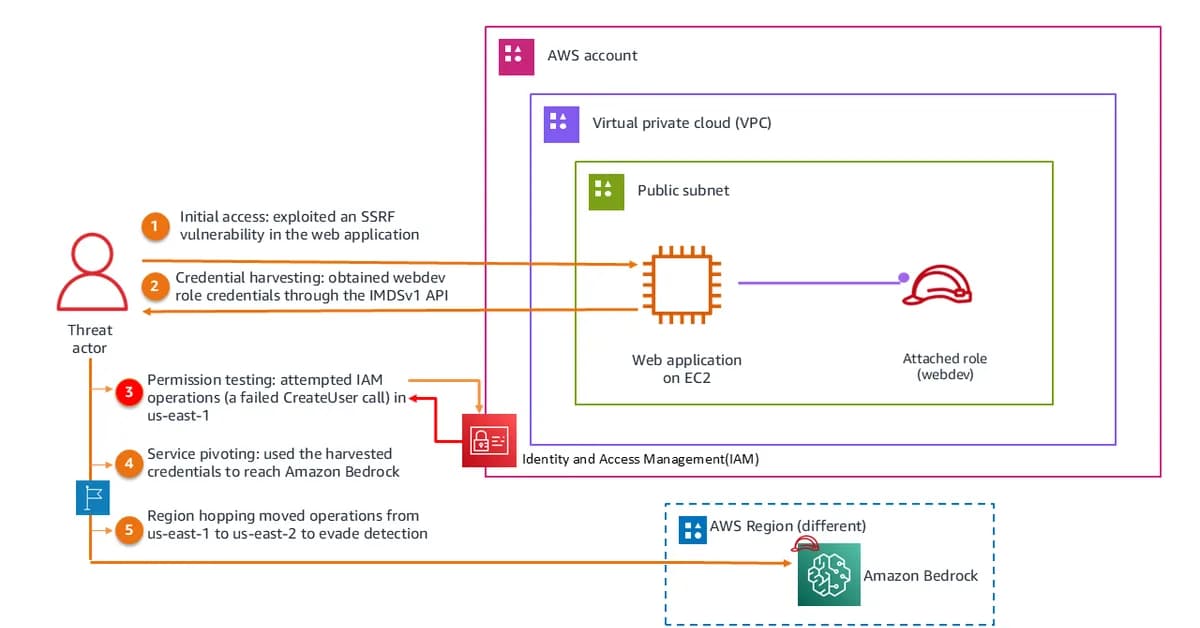
It's clear from the provided log events that the threat actor has successfully pivoted and exploited Amazon Bedrock services after gaining unauthorized access to EC2 instance metadata (IMDS) in us-east-1. Here’s a detailed breakdown of the key points:
Event 1: Unauthorized IMDS Access (15:40:39 UTC)
The attacker accessed the EC2 instance's metadata service, which allowed them to retrieve sensitive credentials such as IAM role and access keys associated with the instance.
Key Insights:
- IMDSv1: The use of IMDSv1 is a critical vulnerability since it does not require MFA for accessing instance metadata.
- Instance ID: The attacker accessed the metadata from
i-0123456789abcdef0, allowing them to trace back the compromised resource.
Event 2: Console Sign-In with Stolen Credentials (17:15:00 UTC)
The threat actor used the harvested credentials to log in to the AWS Management Console, indicating a pivot from programmatic access to visual console interaction.
Key Insights:
- MFA Bypass: The lack of MFA enforcement is crucial since it allowed the attacker to authenticate without additional
Read the full article at AWS Security Blog
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views51
On this page

Ali NematiBlogUI.author_articles