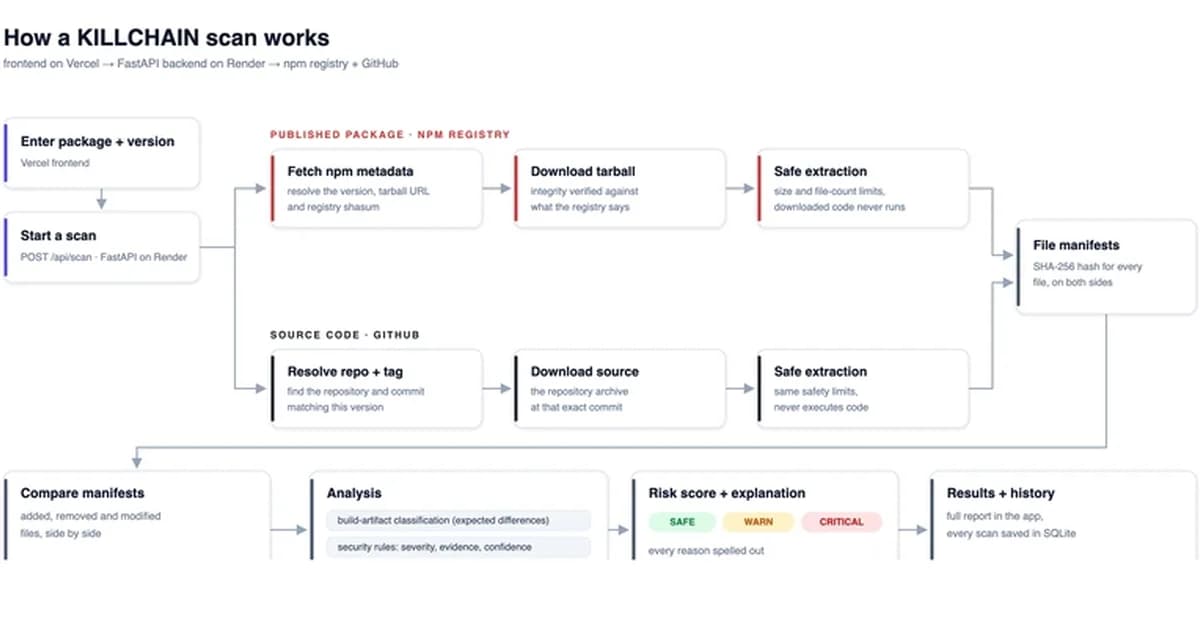
A new tool called KILLCHAIN addresses a critical vulnerability in the software supply chain by verifying that published packages match their source code on GitHub. This is significant for AI/ML/Data Science professionals because it highlights the potential for malicious code to be introduced through dependency management, impacting model integrity and security. The project’s next steps include expanding support to Python's PyPI package repository and implementing continuous monitoring for new package releases.
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views20
Ali NematiBlogUI.author_articles