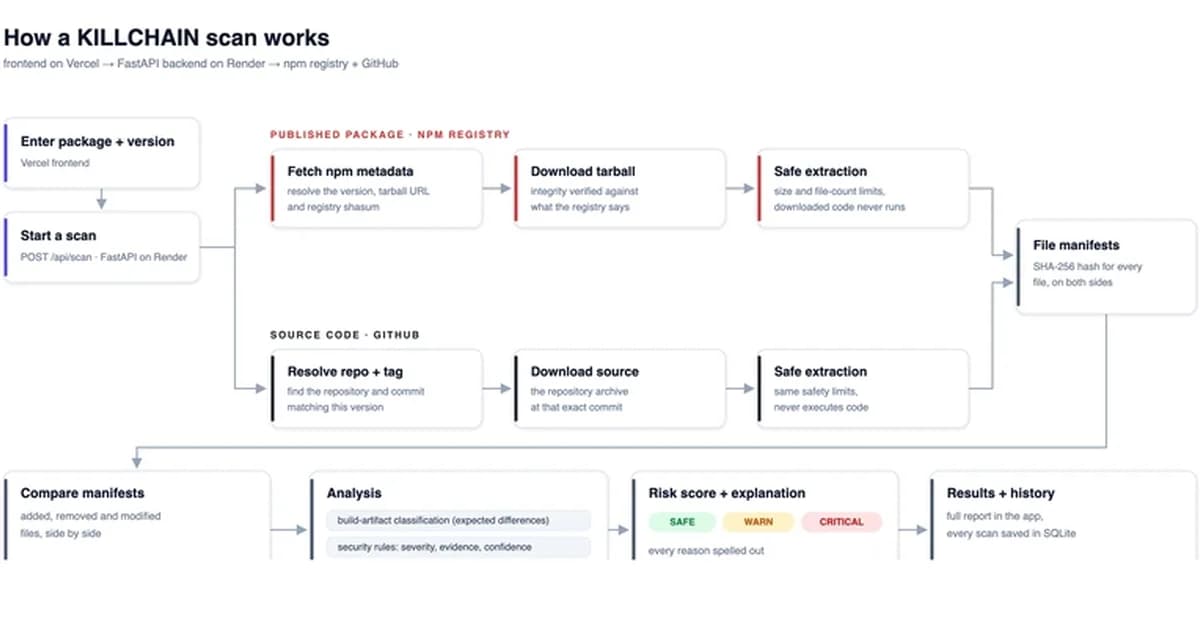
Supply chain attacks targeting developer tools have surged, as evidenced by the LiteLLM PyPI compromise and Trivy GitHub Actions incident. These attacks exploit dependencies to steal credentials and breach data, highlighting a shift in tactics from targeting finished applications to compromising development infrastructure. Developers must now prioritize securing their build environments and dependencies to mitigate such risks.
Read the full article at DEV Community
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views236
Ali NematiBlogUI.author_articles