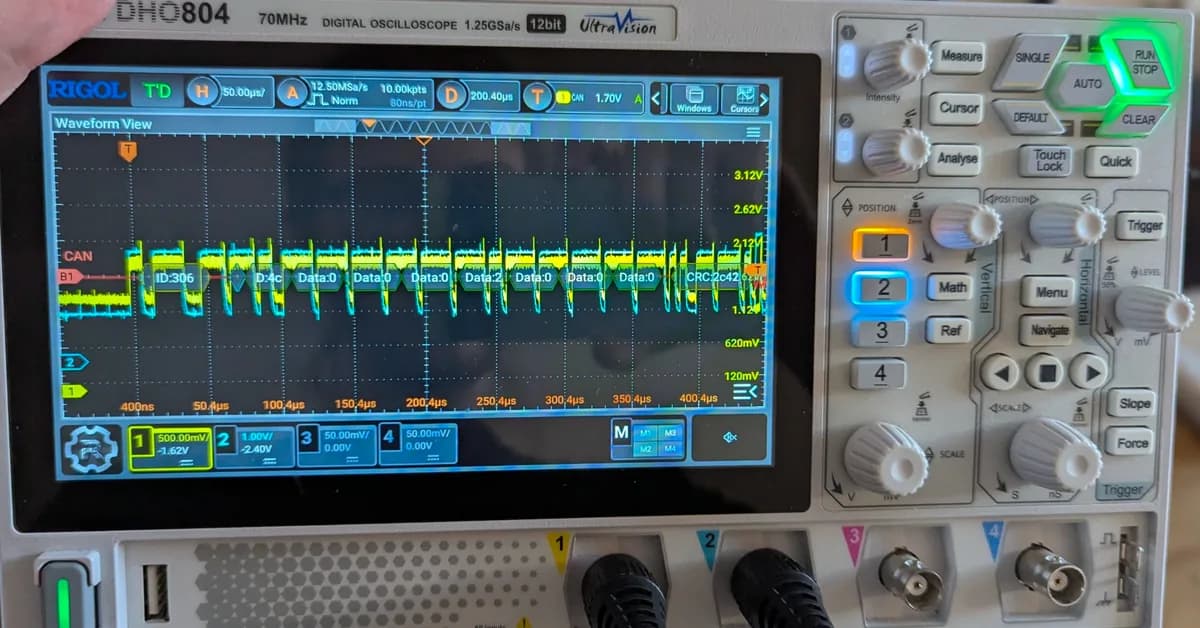
A hobbyist successfully reverse-engineered and rewrote the firmware of an Egret GT E-scooter using Rust, addressing a security vulnerability related to unauthorized access. This development highlights the potential for attackers to exploit weaknesses in connected devices through protocol analysis and firmware manipulation, impacting manufacturers' ability to secure their products. The discovery that the scooter’s CAN bus is accessible via its USB-C port warrants further investigation into similar device designs.
Read the full article at Hackaday
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views58
Tags

Ali NematiBlogUI.author_articles