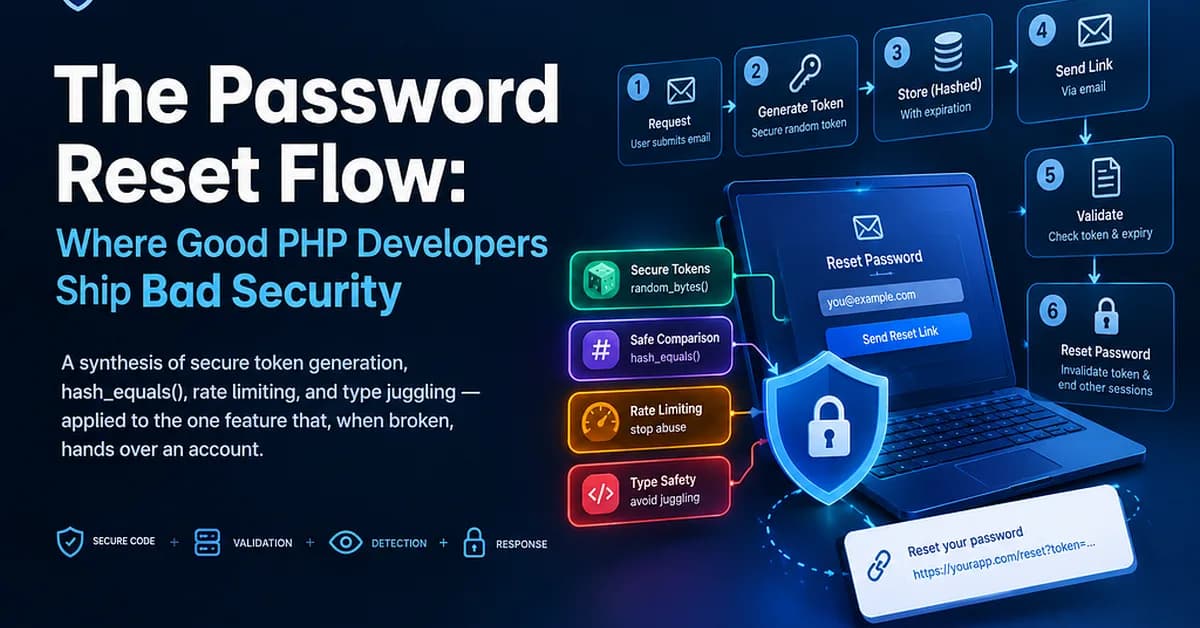
A common vulnerability in password reset flows involves developers incorrectly combining secure token generation, constant-time comparison, rate limiting, and PHP's type system, leading to account takeovers. This is critical for cybersecurity professionals and developers, as it demonstrates how seemingly correct individual code snippets can create significant security holes when integrated improperly into critical functions like password resets. The implication is a need for more holistic security training focused on the interaction of these elements.
Read the full article at System Weakness - Medium
Want to create content about this topic? Use Nemati AI tools to generate articles, social posts, and more.
Views47
Tags

Ali NematiBlogUI.author_articles